Secuwall
Specialized & Emerging Technology

Web3 Application Penetration Testing

Smart contract auditing plus frontend-to-blockchain testing to prevent logic flaws, rug pulls, and liquidity drainage.

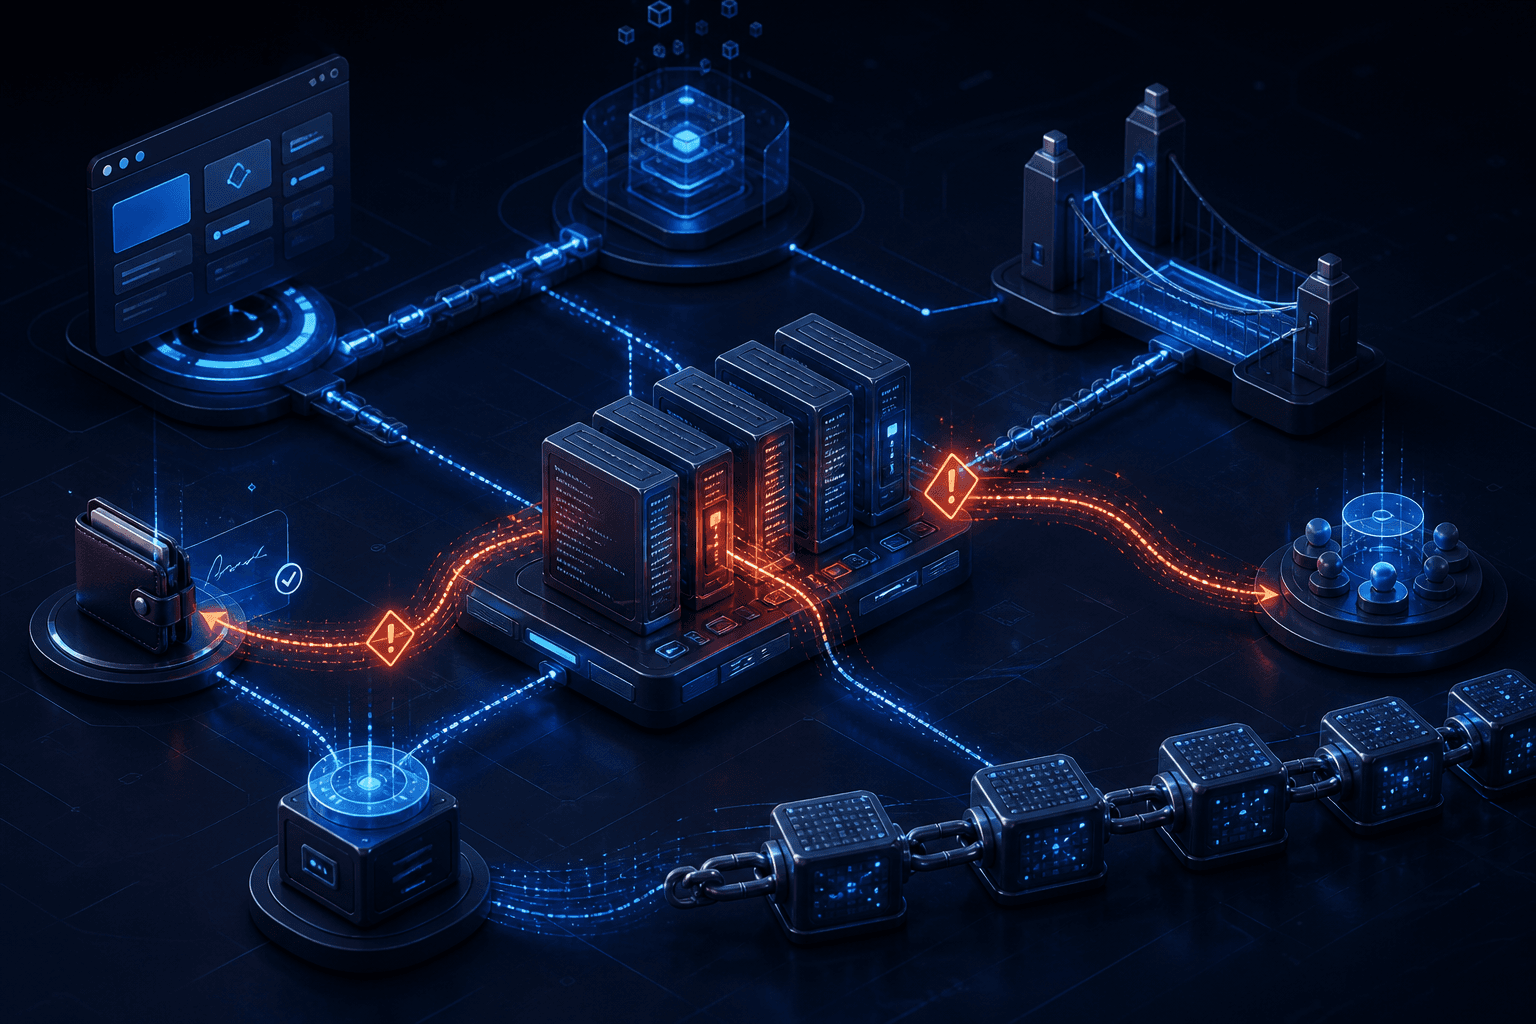
A decentralized application connecting wallets, smart contracts, ledger state and bridge infrastructure
Controlled security analysis

Introduction

Definition

A Web3 Penetration Test is a comprehensive security assessment of a decentralized application (dApp). It is a hybrid methodology that evaluates three core components:

  • The Frontend: The web or mobile interface that users interact with.
  • The Backend (Off-Chain): Traditional APIs, servers, and infrastructure (e.g., RPC nodes) that support the dApp.
  • The Smart Contracts (On-Chain): The immutable business logic deployed to a blockchain (e.g., Ethereum, Solana, Polygon).
Primary Goal

The goal is to identify and exploit vulnerabilities across all three components. The primary focus is often on the smart contracts, where flaws can lead to irreversible, catastrophic financial loss (e.g., draining a protocol's treasury). The test simulates attacks from malicious users, external attackers, and even network-level actors (e.g., miners/validators).

Guiding Frameworks

This methodology is guided by:

  • OWASP Web Top 10: For the frontend and off-chain API components.
  • Smart Contract Security Guidelines (e.g., SWC Registry, Smart Contract Weakness Classification): For the on-chain code.

Penetration Test Phases

Web3 testing across frontend, backend, and smart-contract layers

Phase 1: Planning and Scoping

1.1. Define Objectives

  • Clearly define the goals (e.g., "Drain funds from the treasury," "Mint unauthorized NFTs," "Take over governance," "Access another user's data," "Impersonate the admin").

1.2. Define Scope

  • Smart Contracts (On-Chain):
  • Frontend (Client-Side): In-scope URLs for the dApp (e.g., https://app.example-defi.com).
  • Backend (Off-Chain):
  • Out-of-Scope:

1.3. Establish Rules of Engagement (ROE)

  • TESTNET & FORKS: CRITICAL: All active exploitation and testing must be performed on a specified testnet (e.g., Sepolia) or a local fork (using tools like Hardhat or Foundry).
  • MAINNET IS OFF-LIMITS: No active, exploitative testing is permitted on the main production network.
  • Credentials: Test accounts (with testnet funds) must be provided for all user roles.
  • Communication Channels: A direct line to the development team for critical findings.

Phase 2: Reconnaissance

Gathering information about all three components of the dApp.

2.1. Frontend & Backend Reconnaissance

  • Standard Web Recon: Use traditional tools (nmap, dirb, Burp Suite) to map the web app, find hidden directories, and identify running technologies (e.g., React, Node.js).
  • OSINT: Review GitHub, documentation (whitepapers, developer docs), and social channels (Discord, Telegram) to understand the architecture and find potential leaks.

2.2. Smart Contract Reconnaissance (On-Chain)

  • Block Explorers: Use tools like Etherscan (or PolygonScan, etc.) to:
  • Automated Tools: Use tools like Slither or Mythril to perform an initial, high-level static analysis of the source code to find "low-hanging fruit."

Phase 3: Vulnerability Analysis

This is the core execution phase, broken down by component.

3.1. Frontend (Client-Side) Testing

  • OWASP Top 10: Test for all standard web vulnerabilities (XSS, CSRF, etc.).
  • Web3-Specific Flaws:

3.2. Backend (Off-Chain) Testing

  • API Testing: Test all API endpoints for standard web vulnerabilities (IDOR, SQLi, Broken Access Control, RCE).
  • RPC Node Security: If the RPC node is self-hosted:
  • Is it exposed to the public?
  • Are dangerous API modules (e.g., admin, personal) enabled and exposed?
  • Key Management: Are any private keys or API keys (e.g., Infura, Alchemy) hardcoded in the backend or frontend code?

3.3. Smart Contract (On-Chain) Testing

  • This is the most critical part of the audit, divided into static and dynamic analysis.

3.3.1. Static Analysis (Manual Code Review)

This involves reading every line of the smart contract source code (e.g., Solidity, Vyper) to find vulnerabilities, including:

  • Reentrancy: The #1 vulnerability (e.g., The DAO hack).
  • Integer Overflow/Underflow: (Pre-Solidity 0.8.0).
  • Access Control Flaws: Missing onlyOwner modifiers, public vs. external vs. private.
  • Insecure delegatecall: (Can an attacker hijack the contract's logic?).
  • Business Logic Flaws: Does the math/logic actually do what the whitepaper says it does?
  • Oracle Manipulation: Is the contract using a safe price feed (e.g., Chainlink) or an insecure one (e.g., a single DEX)?
  • Transaction Order Dependency (Front-Running): Can an attacker profit by seeing a user's transaction and submitting their own first?
  • Insecure Randomness: Using block.timestamp or block.hash for randomness.

3.3.2. Dynamic Analysis (Testnet/Fork Testing)

  • This involves actively interacting with the contract on a testnet or local fork.
  • Fuzz Testing: Use tools like Foundry to run thousands of simulated transactions with random inputs to try and break the contract's state.
  • Proof-of-Concept (PoC) Scripting: Write exploit scripts (using Hardhat or Foundry) to confirm the vulnerabilities found in static analysis. (e.g., "Write a test that proves reentrancy by successfully draining the contract").
  • Gas/DoS Analysis: Are there any loops that could lead to an "out-of-gas" error, bricking the contract?

Phase 4: Exploitation

This phase focuses on demonstrating the impact of the vulnerabilities.

  • The "Exploit" is a PoC Script: Unlike a network test, the deliverable is not a reverse shell. It's a runnable script (e.g., a Foundry test) that proves the exploit.
  • Chaining Vulnerabilities:

Phase 5: Reporting

5.1. Impact Analysis

  • Financial Modeling: Quantify the maximum potential loss. "The identified vulnerability allows a full drain of the 10,000 ETH in the protocol's treasury."
  • Governance Hijacking: "The vulnerability allowed us to mint enough governance tokens to unilaterally pass any proposal, effectively taking over the protocol."
  • Systemic Risk: "The flaw in the price oracle could be used to cause a cascading liquidation event across the entire protocol."

5.2. Reporting

  • Executive Summary: A high-level, non-technical summary for management, focusing on the business and financial risk of the findings.
  • Technical Report: A detailed, tactical report for developers.
  • Findings (Prioritized): Each finding must be rated (Critical, High, etc.).
  • Vulnerability Details: A clear description of the flaw (e.g., "Reentrancy in Treasury.sol::withdraw()").
  • Evidence: The Proof-of-Concept script is the primary evidence.
  • Remediation: Provide clear, actionable, and code-specific recommendations.

Phase 6: Remediation and Re-testing

  • Present the findings to the client's team.
  • After the fixes are implemented (and a new commit hash is provided), the audit team performs a re-test to validate that the vulnerabilities are no longer present.